How is software application security testing automated?
Modern software applications handle sensitive information, support business operations, and connect millions of users to digital services. As applications become more complex, protecting them from cyberattacks becomes increasingly important. Manual security checks are valuable, but they can take considerable time and may not identify every vulnerability. 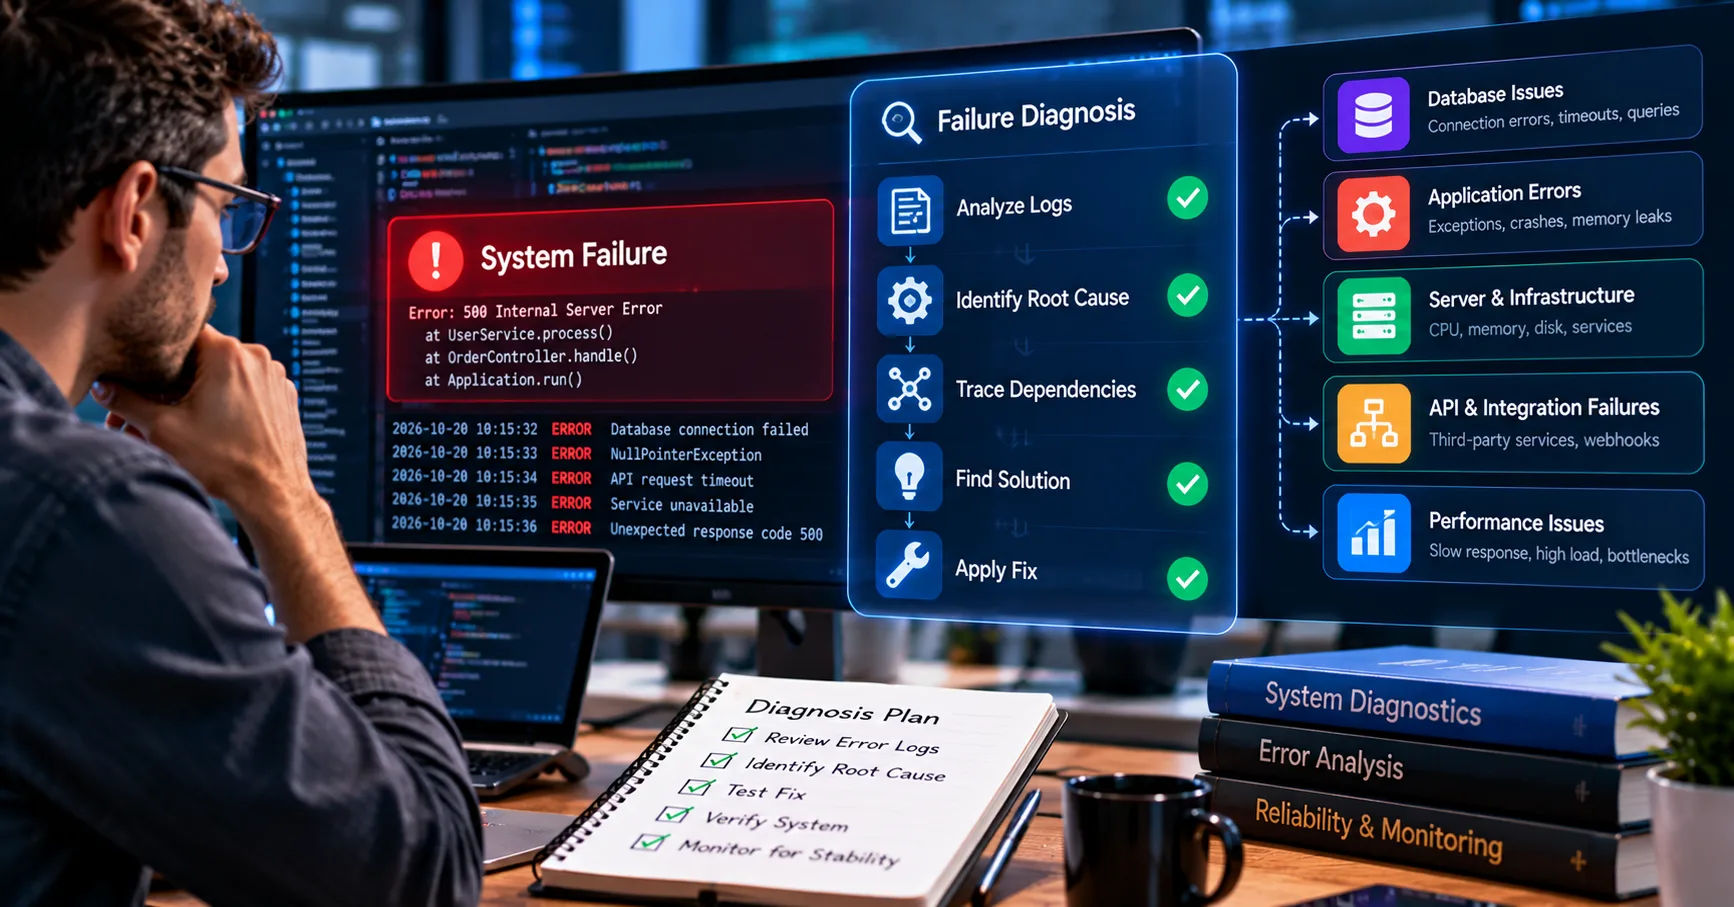 This is why businesses increasingly rely on automated security tools to identify weaknesses throughout the software development process.
Automation makes it possible to examine code, test applications, review dependencies, and detect potential security problems with less manual effort. Software application security testing helps development teams discover vulnerabilities earlier, reduce security risks, and build more reliable applications. By integrating automated checks into everyday development activities, organizations can identify issues before they reach production.
Understanding how automation works is essential for developers, security professionals, and business owners who want to protect their applications. From scanning source code to testing running applications, automated security processes can improve the consistency and speed of vulnerability detection. However, successful automation requires suitable tools, clear testing policies, and experienced professionals who can interpret the results.
What Is Automated Software Application Security Testing?
Automated software application security testing uses specialized software to examine an application for potential security weaknesses. Instead of depending entirely on a person to review every line of code or test every feature, these tools perform predefined checks automatically.
They look for common vulnerabilities, insecure coding practices, configuration mistakes, exposed secrets, and weaknesses in application components. Depending on the testing method, the tools may analyze source code, inspect a running application, or evaluate third-party libraries.
The primary goal is to make security testing repeatable and efficient. Developers can run scans whenever code changes, allowing teams to discover problems before they become expensive to fix.
How Automation Differs From Manual Testing
Manual testing involves security professionals examining application behavior, reviewing code, and investigating possible attack paths. This approach is particularly useful for identifying complex business logic problems and vulnerabilities that require human judgment.
Automated testing follows predefined rules, patterns, and testing techniques. It can process large amounts of code quickly and repeat the same checks consistently.
For example, an automated scanner may identify a database query that appears vulnerable to SQL injection. A security specialist can then investigate whether the issue is exploitable and determine the appropriate correction.
The most effective security programs combine automated tools with manual analysis rather than treating either approach as a complete solution.
How Does the Automation Process Work?
Automated security testing generally follows a structured process. Although individual tools operate differently, most systems use several common stages to discover vulnerabilities and communicate their findings.
1. Identifying the Application and Its Components
The first step is understanding what needs to be tested. Teams identify the application, its source code, programming languages, frameworks, APIs, external services, and third-party dependencies.
This information helps testing tools determine which checks are relevant.
For example, a web application built with JavaScript and Python may require different analysis rules from a mobile application developed with Kotlin. An application that uses a database or payment gateway may also need additional security checks.
A clear inventory helps teams avoid overlooking important components.
2. Selecting Appropriate Testing Tools
Different tools identify different categories of security problems. Organizations usually select tools according to their technology stack, development workflow, application architecture, and risk level.
Some tools analyze source code, while others inspect running applications or examine open-source packages for known vulnerabilities.
Teams may use several tools together to improve coverage. However, choosing more tools does not automatically produce better security. The selected solutions must work together, provide useful findings, and fit the development team's workflow.
3. Running Automated Scans
After configuration, the tools examine the selected application components.
A source-code scanner might search for unsafe functions, weak cryptographic practices, or potentially dangerous data handling. A dynamic scanner may send requests to a running application and observe how it responds.
Scans can run on a schedule, whenever developers submit code, or before a release is approved.
The results usually include potential vulnerabilities, their locations, severity ratings, and recommendations for remediation.
4. Evaluating and Prioritizing Findings
Automated tools can generate many findings, but not all of them represent equally serious risks.
A weak password policy, exposed authentication token, and minor information disclosure do not necessarily have the same impact.
Teams prioritize vulnerabilities by considering factors such as exploitability, potential damage, affected data, exposure to the internet, and the importance of the affected system.
This process helps developers address critical issues before spending time on less significant findings.
5. Fixing Problems and Testing Again
Once a vulnerability has been confirmed, developers correct the underlying issue. The automated tool then runs another scan to check whether the problem has been resolved.
This repeated process creates a feedback loop that supports continuous improvement.
For example, after correcting an insecure input-handling function, a developer can run the same security check again. If the finding disappears and relevant tests pass, the team gains evidence that the correction worked.
Major Types of Automated Security Testing
Several testing methods support application security automation. Each method focuses on a different part of the software lifecycle.
Static Application Security Testing
Static Application Security Testing, commonly called SAST, examines source code, bytecode, or compiled application components without requiring the application to run.
It searches for patterns associated with insecure programming practices, including unsafe input handling, hardcoded credentials, and improper data validation.
SAST tools can be integrated into code editors, repositories, and continuous integration pipelines. Developers may receive warnings while writing code or when submitting changes for review.
An important advantage is early detection. Problems discovered during development are often easier and less expensive to correct than issues found after deployment.
However, static scanners may report false positives or miss vulnerabilities that depend on actual runtime behavior.
Dynamic Application Security Testing
Dynamic Application Security Testing, or DAST, examines an application while it is running.
The scanner interacts with the application through its web interface, APIs, or other accessible endpoints. It sends requests and analyzes responses to identify potential weaknesses.
Depending on its capabilities, a DAST tool may test for SQL injection, cross-site scripting, insecure headers, and certain authentication or configuration problems.
Because it examines a running system, DAST can reveal issues that are difficult to identify through source-code analysis alone.
Its limitations include incomplete application coverage, authentication challenges, and difficulty reaching features hidden behind complex workflows.
Software Composition Analysis
Modern applications rely on third-party libraries, frameworks, and open-source packages. These components can contain known security vulnerabilities even when the organization's own code is well written.
Software Composition Analysis, or SCA, automatically identifies dependencies and compares them with vulnerability databases and package information.
For example, an application might use an outdated library with a publicly documented security flaw. An SCA tool can flag the affected version and recommend a safer release.
Some tools also identify licensing concerns and outdated packages.
Keeping dependencies current is an important part of automated security because vulnerabilities can enter an application through external components.
Interactive Application Security Testing
Interactive Application Security Testing, known as IAST, analyzes application behavior while the software runs under instrumentation.
It combines aspects of code analysis and runtime testing. The tool observes how data moves through the application and identifies potentially unsafe operations during test execution.
IAST can provide useful information about where a vulnerability occurs and how user input reaches the affected code.
However, its effectiveness depends on the test cases executed and the application features covered during those tests.
How Automation Fits Into the Software Development Lifecycle
Security automation becomes more effective when it is integrated into the development process instead of being treated as a final inspection.
Integration With Continuous Integration and Continuous Delivery
Continuous Integration and Continuous Delivery, commonly abbreviated as CI/CD, automate activities such as building, testing, and deploying software.
Security tools can become part of these automated pipelines. Whenever a developer submits a change, the pipeline can run selected security checks before allowing the change to progress.
For example, a pipeline might perform static analysis, inspect dependencies, execute unit tests, and then deploy the application to a testing environment for dynamic scanning.
If a critical vulnerability is detected, the pipeline can stop the release until the issue is investigated or resolved according to the organization's policy.
This approach makes security a routine development responsibility rather than a separate task performed shortly before launch.
Security Checks During Code Reviews
Automated tools can examine proposed code changes and display security findings directly in pull requests or code reviews.
Developers can see which lines may contain problems and understand why a change requires attention.
This shortens the feedback cycle because developers do not need to wait for a separate security review to discover every issue.
Teams can also establish rules that prevent certain high-risk changes from being merged without approval.
Automated Testing Before Deployment
Before software reaches production, automated testing can evaluate the application in a controlled environment.
Teams may combine vulnerability scans, configuration checks, dependency reviews, and authentication tests to assess release readiness.
The exact requirements depend on the application's purpose and risk level. A public banking platform may require stricter controls than an internal informational website.
Testing before deployment reduces the likelihood that known vulnerabilities will reach users.
What Security Vulnerabilities Can Automation Detect?
Automated tools can identify many common security weaknesses, although their coverage varies by tool and configuration.
Injection Vulnerabilities
Injection vulnerabilities occur when an application handles untrusted input unsafely. Examples include SQL injection and certain command injection flaws.
Static scanners may identify risky query construction, while dynamic scanners can test whether crafted inputs produce suspicious behavior.
Parameterized database queries, appropriate input handling, and secure API design help reduce these risks.
Cross-Site Scripting
Cross-site scripting, or XSS, occurs when an application allows untrusted content to execute as script in another user's browser.
Automated testing tools may detect unsafe output handling, missing contextual encoding, or responses that appear to execute injected content.
Developers should use context-aware output encoding and suitable framework protections to prevent malicious scripts from running.
Authentication and Access Control Issues
Security tools can test certain authentication weaknesses, insecure session handling, and access control problems.
For example, a scanner may identify a protected page that appears accessible without proper authentication.
However, complex authorization flaws are particularly difficult to detect automatically. A tool may not understand that one user should never access another user's records unless it has been configured with suitable test accounts and access rules.
Exposed Secrets and Insecure Configurations
Automated secret scanners search repositories for passwords, API keys, private keys, and other sensitive credentials.
Configuration scanners can identify issues such as unnecessary open services, weak security settings, or missing protective headers.
When a secret is exposed, deleting it from the latest version of the code is not enough. The credential should generally be revoked or rotated, and its exposure should be investigated.
Benefits of Automating Application Security Testing
Automation offers several practical advantages for organizations that develop and maintain software.
Faster Vulnerability Detection
Automated scanners can examine large codebases much faster than a person can review every component manually.
Frequent scanning helps teams discover vulnerabilities soon after they are introduced. This makes investigations more focused and corrections easier to manage.
Consistent and Repeatable Results
Manual reviews may differ depending on the tester, available time, and scope of the review.
Automated checks can apply the same rules across many projects and development environments. This consistency supports clearer security standards and more reliable reporting.
Lower Long-Term Remediation Costs
Security problems can become more expensive when they remain undetected until deployment or exploitation.
Finding vulnerabilities during coding or testing often allows developers to correct them before they affect customers, business operations, or sensitive information.
Automation also reduces repetitive checking, allowing security professionals to focus on complex problems that require specialized expertise.
Better Collaboration Between Teams
When security findings appear in existing development tools, developers can address them as part of their normal workflow.
Clear reports, severity ratings, and remediation guidance help development and security teams communicate more effectively.
This approach supports a culture in which application security is shared across the organization.
Challenges and Limitations of Security Automation
Although automation improves efficiency, it does not guarantee that an application is secure.
False Positives and False Negatives
A false positive occurs when a tool reports a potential vulnerability that is not actually exploitable under the relevant conditions.
A false negative occurs when a genuine vulnerability goes undetected.
Too many false positives can overwhelm developers and reduce confidence in security reports. False negatives can create a misleading impression that the application is safe.
Teams should tune their tools, validate important findings, and use multiple testing approaches where appropriate.
Limited Understanding of Business Logic
Automated scanners may struggle to understand complex application rules.
For example, a shopping platform could allow a customer to change an order's price through an unusual sequence of actions. Detecting such a flaw may require understanding how pricing, discounts, permissions, and order processing are intended to work together.
Manual penetration testing and targeted security reviews remain valuable for these situations.
Tool Configuration and Maintenance
Security tools require proper configuration, regular updates, and ongoing review.
An incorrectly configured scanner may overlook important endpoints or repeatedly report irrelevant issues. Outdated vulnerability databases may also miss newly disclosed problems.
Organizations should assign responsibility for maintaining testing rules, reviewing scan coverage, and updating integrations.
Potential Performance and Workflow Issues
Running every possible security test after every small code change may slow development pipelines.
Teams can address this by using faster checks during routine coding and reserving more comprehensive scans for scheduled testing or release preparation.
The objective is to maintain meaningful security coverage without creating unnecessary delays.
Best Practices for Successful Security Automation
Organizations can improve their results by adopting a structured approach to automation.
Start With High-Risk Areas
Begin by identifying applications, data, and components that would cause the greatest harm if compromised.
Prioritize authentication systems, payment processing, sensitive databases, public APIs, and critical business functions.
This helps teams allocate testing resources according to actual risk rather than treating every component as equally important.
Combine Multiple Testing Methods
No single tool can detect every vulnerability.
A strong testing strategy may combine SAST for code analysis, DAST for runtime behavior, SCA for dependencies, secret scanning for exposed credentials, and configuration analysis for deployment weaknesses.
Manual reviews should complement these automated methods when business logic or complex attack paths require deeper investigation.
Establish Clear Security Policies
Organizations should define which findings block a release, who reviews exceptions, and how quickly vulnerabilities must be addressed.
For example, critical vulnerabilities may require immediate investigation, while lower-risk issues can follow an agreed remediation schedule.
Clear policies prevent important findings from being ignored and help teams apply security requirements consistently.
Measure Results and Improve Continuously
Useful metrics include the time required to fix vulnerabilities, the number of recurring findings, scan coverage, and the percentage of high-risk issues resolved before deployment.
Teams should interpret these measurements carefully. A high number of detected vulnerabilities does not always mean security is worsening; it may reflect improved detection.
Regular reviews help organizations identify gaps and refine their automated testing process.
Conclusion
Automating application security testing allows organizations to identify vulnerabilities earlier, apply consistent security checks, and reduce the manual effort required to protect software. By analyzing source code, inspecting running applications, checking dependencies, and examining configurations, automated tools help development teams discover many common weaknesses before they reach production.
However, effective software application security testing requires more than installing a scanner. Organizations must select appropriate tools, integrate them into development workflows, prioritize findings according to risk, and verify that important vulnerabilities have been corrected.
The strongest approach combines automation with human expertise. Automated systems handle repetitive checks and provide rapid feedback, while security professionals investigate complex weaknesses, validate findings, and assess risks that tools may not fully understand.
Businesses should begin with their highest-risk applications, establish clear testing policies, and gradually expand their automated coverage. They should also keep tools updated, monitor recurring vulnerabilities, and review the effectiveness of their security controls regularly.
When implemented thoughtfully, software application security testing becomes an ongoing part of software development rather than a last-minute requirement. This approach helps organizations build more dependable applications, protect sensitive information, respond to emerging threats, and maintain user trust as their systems evolve.